
According to the report, the Main Radio Frequency Center (GRFC) under Roskomnadzor recommended that telecom operators urgently inspect MikroTik routers used in their networks and warned users to take appropriate measures due to hacker threats due to vulnerabilities in RouterOS. erythrocyte.
According to RBC, industry players began receiving warning letters from regulators on September 11. Prior to this, the CERT Polska team Found RouterOS has six vulnerabilities affecting the SSH server and client, the bandwidth testing service, the X.509 certificate handling mechanism, and the WebFig interface. If remote access via SSH is enabled, the combination allows an attacker to take full control of the device without authentication. The chain is called MikroTrick.
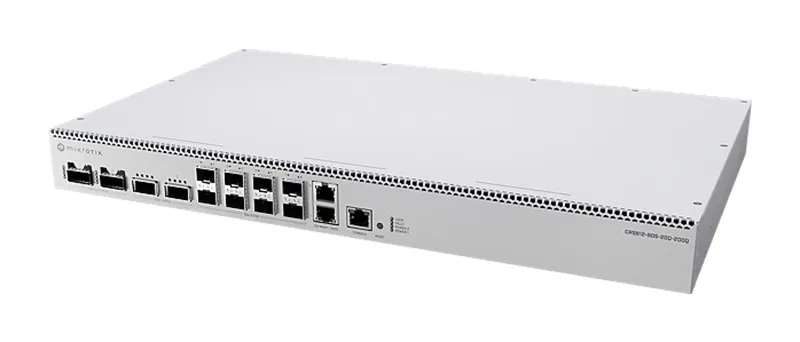
Image source: MikroTik
The most serious of these vulnerabilities are:
- CVE-2026-67276 – SSH authentication bypass (CVSS:9.2);
- CVE-2026-86060 – Privilege escalation in an SSH session via a crafted username (CVSS: 9.2);
- CVE-2026-67277 Memory leak and crash via bandwidth testing service (CVSS: 8.8).
MikroTik announced the release of RouterOS 7.25 beta 3, 7.24.2, 7.23.4 and 6.49.21 updates on September 3 to address identified security vulnerabilities in the operating system, emphasizing that this issue does not pose an immediate threat to ordinary users of home devices, but it is still recommended that all users update. The company also recommends that administrators update their devices as soon as possible and then check the configuration of unknown users, scripts, scheduler tasks, agents, and tunnels.
Polish CERT reports that they have recently recorded attacks on devices running RouterOS and accessible over the network. Attackers have been confirmed to be using a combination of MikroTrick vulnerabilities to gain full control over unprotected devices. Released patches have also been proven to prevent such attacks.
Market participants said it is not the responsibility of telecom operators to update the firmware of users’ routers. But they are responsible for the security of their own networks and can limit dangerous traffic by blocking certain router ports without disconnecting users from the network.
source: