
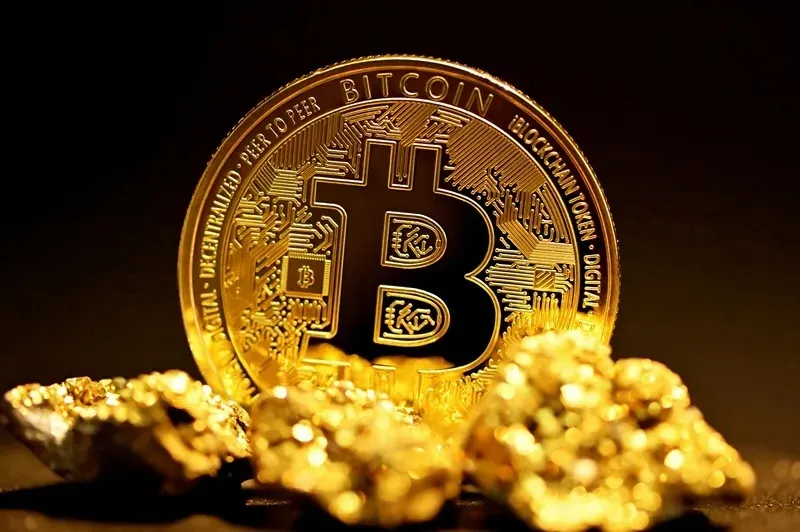
Recently, the Bitget cryptocurrency exchange suffered a hacker attack, and the attackers stole approximately $388 million in cryptocurrency. Bitget CEO Gracy Chen said the platform is trying to track and return assets, but so far it has only been able to identify and freeze $1.1 million worth of cryptocurrency, but not necessarily all of it has been returned to the exchange. The exact amount of the refund was not specified.
Image source: Kanchanara/unsplash.com
Chen said in an interview with a CNBC reporter “No majority of funds expected to be returned”citing statistics on asset recoveries from similar incidents in the past. At the same time, she pointed out “Exchanges are responsible for how they protect their users, especially when things go wrong.”.
The company reported that user accounts were not affected by the hack. Before the incident, the exchange valued its security fund at more than $464 million. Sources said that after the hack, the funding was reduced to less than $200 million, and later recovered to more than $300 million. Chen clarified that the replenished funds can still be publicly verified on the blockchain and are separate from the reserves used to maintain customer account balances.
“We restored the funds using Bitget’s own funds. Bitget bears the financial consequences rather than passing them on to our users.”Chen said.
As for the investigation into the incident itself, previous reports from Mandiant (part of Google Cloud) and SlowMist indicate that the attackers compromised two third-party security products before being able to access Bitget systems. SlowMist experts tracked the earliest malicious activity in available logs as of August 31. The attacker then exploited a zero-day vulnerability in one of the security products. The attackers then gained internal access privileges and were able to bypass the normal process of withdrawing customer funds, but the wallet’s private keys were not stolen.
“I would say the method is quite complex”Chen commented on the incident. She added that the investigation was complicated by the fact that the attackers deleted traces of their presence after making the transfer.
None of the investigative reports revealed which security products were affected by the hack. When asked about the issue, Chen declined to reveal more information about the supplier or the product itself, citing the potential for additional threats if such information were made public. The report did not attribute the cyber attack to North Korean hackers. However, Chen has previously said that the preliminary technical indicators are highly consistent with known groups in North Korea. “We will have to wait for more details on this matter.”Chen added.
If you find an error, select it with your mouse and press CTRL+ENTER.