
Amid a general surge in vulnerability discovery activity driven by the use of artificial intelligence across the software ecosystem, Intel appears to have ended its bug bounty program. At the same time, the company launched a new program to accept vulnerability reports without paying money.
It appears that Intel has closed the previous Bug Bounty program and opened a new Bug Bounty program that does not provide rewards for discovered bugs. The company previously collaborated with Intigriti Platform on a program covering hardware, software, firmware, open source projects, and more. Under the previous plan, payments ranged from $500 to $100,000.
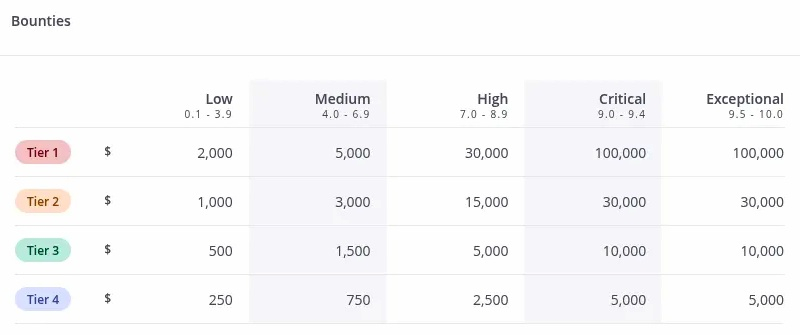
Image source: Intel
The Intigriti page hosting the Intel program now states that the program has been suspended. Much of the previous information has also been removed from the page. Meanwhile, Intel has launched a new program at Intigriti, whose description says: “This is a responsible disclosure program with no monetary reward.”.
There has been no official comment on the reasons for these changes. However, given that the Linux kernel and other open source projects are now literally rife with reports of AI-generated vulnerabilities, this situation played a role in the decision.
If you find an error, select it with your mouse and press CTRL+ENTER.